Mudra Electronics Ltd. — Argus AI Camera for Border Surveillance
Mudra Electronics Rugged AI
cameras
{{ menuLabel }}
Solutions
01 Argus AI cameras Low-signature AI cameras for remote surveillance.
02 Cybersecurity & networks Security monitoring and critical network engineering.
03 Vidura AI SOC Your security team, always on.
{{ n.label }}→
Talk to us→
Argus · AI camera for remote surveillance

Built to keep watch where people find it hard to stay.

Argus is an unattended, low-signature AI camera. It wakes on movement, checks what it sees on the device and alerts headquarters only when your rules are met. Designed to run a year on a single charge.

Explore Argus→
12+ mo
Battery design target · no solar
53ms
Per-frame detection on the device · measured
3
Radio options · cellular available now
−30/+55
°C design range · IP67 design target
01 — The problem

Locations once patrolled twice a year are now monitored by Argus 24/7.

15,107km
Land border · 7 neighbours
7,517km
Coastline · incl. islands
Bangladesh4,096.7
China3,488
Pakistan3,323
Nepal1,751
Myanmar1,643
Bhutan699
Afghanistan*106

Land border in km, Ministry of Home Affairs. About 6,100 km of coastline is mainland; the rest is the Andaman & Nicobar and Lakshadweep islands. *India’s claimed border, via Pakistan-occupied Kashmir.

2–4×

Some high passes can be reached on foot only a few times a month, and only in the warmer months. In winter, snow can close them entirely. (Indicative figure.)

Obscured

Forest canopy, monsoon cloud, fog and snow can limit observation from drones and aircraft, sometimes for weeks.

Noisy

Conventional camera traps need regular battery changes, and the visits can reveal their position. Many also alert on animals, wind and friendly patrols.

→

What is needed: a camera that operates for long periods, is hard to detect, works across the expected climate range and needs few maintenance visits.

02 — How it works

Dormant until needed. Shares only relevant alerts.

01 · DETECT

Motion detection

A low-power motion sensor, with an optional ground vibration sensor, monitors continuously. The camera, processor and radio stay off until needed.

02 · CAPTURE

Image capture

The low-light camera takes three to four photographs, using infrared lighting at night that is invisible to the eye. The optional thermal camera switches on only when needed.

03 · DECIDE

On-device analysis

The on-device AI classifies what it sees (person, vehicle or animal), runs a second check, and looks for a friendly patrol tag before anything is saved or sent.

04 · REPORT

Prioritised alerts

The radio switches on only when an alert meets your rules. It sends a short, encrypted message with a photograph, location and time, then returns to low-power mode.

03 — What it recognises

Transmitted information and decisions stay with authorised operators.

Argus classifies what it sees and checks it against rules you configure, with no cloud connection needed. Operators receive prioritised alerts instead of every movement.

{{ fe.label }}
{{ m.label }}
{{ c.label }}
Simulated camera view · for illustration
What it recognises
{{ d.label }} {{ d.status }}
Configurable responses
Alarm, siren & strobe
Local deterrent when a rule is met
Gate or door lock (integration)
Lock an entry point when a rule is met
Wake nearby cameras
Prepare the next camera along the route
Urgent alert to HQ
Photograph, classification, location and time
Log only
Tagged patrols and animals are logged; no alert is sent
04 — Connectivity

Camera footprint stays the same. Choose the radio that fits your requirements.

The same core platform supports each radio as a plug-in module. Headquarters receives alerts in the same format, whichever radio is fitted.

01Available

Cellular

GSM, 4G and LTE-M on a local SIM. An alert and photo typically reach headquarters in about 30 seconds, depending on coverage.

Near posts & roads with coverage
02In development

Satellite

Direct-to-satellite link with a concealed antenna, for isolated sites with no network. Target delivery time: 1–3 minutes (target).

Designed for Indian-operated satellite services
03Roadmap

LoRa mesh

Cameras pass alerts to each other over encrypted long-range radio. A relay on high ground forwards them to headquarters, so a group of cameras can share one connection.

One relay can connect a group of cameras
05 — Friendly patrol identification

Knows your patrol from a stranger.

Patrol members carry a small coded tag, about the size of a coin. When Argus detects a person, it checks for a valid tag before deciding whether to send an alert.

○ Tagged patrol

Logged with tag number and time. No alert is sent, and headquarters keeps a record of patrol movement.

● Untagged person

An alert is sent to headquarters with a photograph, location and time. An untagged person is not assumed to be hostile: operators review the alert and decide how to respond.

Designed to reduce alerts from friendly patrols · fewer transmissions · lost tags can be cancelled from headquarters
06 — Where it works

Designed for terrains where patrols find it hardest to operate.

All applications →
{{ e.n }}
{{ e.title }}
{{ e.short }}
{{ e.status }}
Also from Mudra

The networks and cyber defence behind the sensors.

Since 1987, Mudra has built and supported critical networks and systems, and today provides managed cybersecurity services. The team that secures Argus communications can support the rest of your organisation too.
Cyber & networks →
Product · low-signature AI surveillance camera

ARGUS

One sealed core, a choice of radio, and a housing matched to the terrain. Use the options below to change the configuration; drag the model to rotate it.View the Argus deck↗

Drag to rotate
{{ v.label }}
{{ explodeLabel }}
Terrain housing
{{ s.label }}

{{ shellNote }}

Radio
{{ v.id }} {{ v.name }}
{{ sel.id }} · {{ sel.name }}
{{ sel.status }}
Connection
{{ sel.link }}
Best for
{{ sel.best }}
Each alert sends
{{ sel.data }}
To HQ
{{ sel.latency }}
Antenna
{{ sel.antenna }}
Day · night · thermal

Day, night and thermal imaging. One platform.

Colour images by day and infrared images at night, with an optional thermal camera that detects body heat. Thermal can see through light smoke and some foliage, but not through dense cover or water. The same AI analyses images from all three modes.

{{ te.label }}
Day · low-light camera
Night · invisible infrared
Thermal · optional module
Capabilities

Proven detection today. A roadmap to eight capabilities.

All run on the camera’s built-in AI processor, without a cloud connection. One capability is available today. The others are in development, or need additional software, sensors or integration.

Available now1
01
Detect
Distinguishes people and vehicles from animals, to reduce alerts caused by wildlife.
53 ms per frame · measured
In development or training6
02
Body posture
Tracks 17 points on the body to recognise climbing, crawling, loitering or a fallen person.
~55 ms · estimate
03
Precise outline
Outlines each person or vehicle precisely, for more accurate restricted zones and counts.
~63 ms · estimate
04
Secondary classification
A second check on each detection: uniform or civilian, which animal, and whether it is really a person.
~15 ms · estimate
05
Movement rules
Line crossing, direction of travel, people counting and time spent in an area.
A few ms · estimate
06
Actions over time
Recognises behaviour over several seconds, such as a person falling or crawling.
Not yet tested
07
Sound
Detects sounds such as gunshots, vehicle engines and breaking glass, including events outside the camera’s view.
Not yet tested
Hardware supported · needs integration1
08
Second camera
Pairs day with thermal, or wide-angle with zoom, inside the same unit. Needs additional software and sensor integration.
Hardware supported
53 ms: measured per frame on the built-in AI processor; hardware and test conditions to be published. Other times are engineering estimates and have not yet been measured with the same method.
Sensors

Argus watches the terrain more closely than any patrol can.

A 40° lens suits trails and narrow crossings; a 25° lens suits longer approach paths. For 50–150 m, the narrow lens is paired with a longer-range sensor. Ranges are design targets.

Low-light camera
STANDARD
2 MP sensor with 940 nm infrared lighting, which is invisible to the eye and harder for many night-vision devices to detect than 850 nm lighting.
Thermal camera
OPTION
Detects body heat, including through light smoke and some foliage. Switches on only when needed, to save battery. 384×288 or 640×512 resolution.
Motion sensor
STANDARD
Passive infrared (PIR), always on at very low power. Typical detection range 15–25 m.
Ground sensor
OPTION
Buried vibration sensor that detects footsteps and vehicles beyond the motion sensor’s range.
Evidence
ALL VARIANTS
Full-resolution photographs stored encrypted, with GPS location and time. Collected by patrol or requested remotely by headquarters.
Endurance

Designed to last a year on a single charge. Fewer visits, fewer footprints.

Engineering estimate, pending endurance testing. Assumptions: one 170 Wh cold-rated battery, cellular radio, about 10 alerts a day, no solar. Fewer battery changes mean fewer site visits and less chance of revealing the camera’s position.

Battery life depends on the radio fitted, the alert rate and the temperature. An optional solar panel can extend operation at busy sites.

Security & qualification

If it’s taken, the data isn’t.

Signed software
Designed to accept only signed, approved software and AI updates.
Encrypted, AES-256
Designed to encrypt stored photographs and radio links with AES-256, with a separate key for each camera.
Tamper wipe
If the unit is opened or moved, it is designed to send a final alert and erase its encryption keys, protecting stored data.
Radio silence
Headquarters can switch the radio off or set a transmission schedule. Alerts are stored and sent later.
MIL-STD-810H · environmental · design reference MIL-STD-461G · EMI/EMC · design reference IEC 60529 · IP67 · design target Formal qualification testing pending

The full Argus briefing, slide by slide.

Open the Argus deck↗
Request an evaluation
Applications

One platform. Configured for each environment.

The same AI core, configured for each location with a terrain-specific housing, sensors and radio. Each scenario shows where it is deployed, what Argus does there, why it helps, and which parts are available today.

{{ e.caption }}
{{ e.n }} {{ e.status }}

{{ e.title }}

Where{{ e.where }}
What it does{{ e.does }}
Why it helps{{ e.why }}
Availability{{ e.avail }}
{{ t }}
Facing an active incident?
Cyber cell desk · mel@mudraindia.com →
Cybersecurity & network engineering

Security for networks that can’t go down.

Mudra helps defence, government and enterprise organisations protect their networks, systems and sensitive data. Our services cover security monitoring, threat detection and response, data loss prevention, secure network access and critical-infrastructure protection, built on engineering experience dating back to 1987. Our new AI security operations centre, Vidura, runs entirely in India.

Request a security assessment→
Explore Vidura↓
See all capabilities
Two-week assessment · Fixed scope · You keep the findings
Global threat activity · indicative
Illustrative view · not live data
Illustrative counter
0

Threat activity extends across networks worldwide. Most organisations now defend systems far beyond their own buildings.

1987
Year founded
39yrs
In engineering & integration
500+
Deployments delivered
30+
Defence & government entities served
01 — The problem

More alerts. Fewer people to read them.

Staff, contractors and systems now work from homes, partner sites and cloud services, outside the traditional firewall. At the same time, the number of security tools, and the alerts they produce, has grown faster than the teams available to review them.

Large organisations often address this with large in-house security teams. Mid-size enterprises, government departments and utilities running older operational technology alongside new connected devices face similar threats with far fewer people.

Mudra provides experienced cybersecurity support, tailored to your organisation.

02 — Product · AI security operations centre (AI SOC)
Design-partner programme open

Vidura.
Your security team, always on.

Vidura watches your network 24×7, explains what it finds in plain language, and makes changes only when you approve them.

Why “Vidura”? In the Mahabharata, Vidura was the king’s most trusted adviser. He saw what others missed, spoke plainly, and advised rather than acted alone.

Sees the whole networkFirewalls, computers, servers, cloud and AI tools.
Explains in plain languageA map and clear answers instead of log files.
Acts only with approvalOne tap to approve. Every change can be undone.
Uses your existing toolsWorks with the security products you already own.
Stays in IndiaOn your premises, in Indian cloud, or fully offline.
Vidura hardware · your AI defender in a box

Plug it in. It guards your network.

Vidura is your own AI security team in one sealed box. It maps every device, watches 24×7, explains what it finds in plain language and acts when you approve. You simply talk to it.

YOUR NETWORK SERVERS Data centre LAPTOP Accounts ALERT ISOLATED CCTV Gate 2 WI-FI Office FIREWALL Perimeter CLOUD Email PHONES Staff PRINTERS Floor 3
VIDURA · CHATWATCHING 24×7
What’s happening on my network today?
VIDURA
All 148 devices checked. One laptop in Accounts started sending files to an unknown server at 2:14 a.m.
VIDURA
I recommend cutting it off from the network and keeping a copy of the evidence. Shall I go ahead?
APPROVEEXPLAIN MORE
Approve.
VIDURA
Done. The laptop is isolated, IT has a ticket, and your morning report explains what happened.
01
Plug it in
02
It maps your network
03
Ask in plain language
04
Approve. It acts.
Illustration · sample network
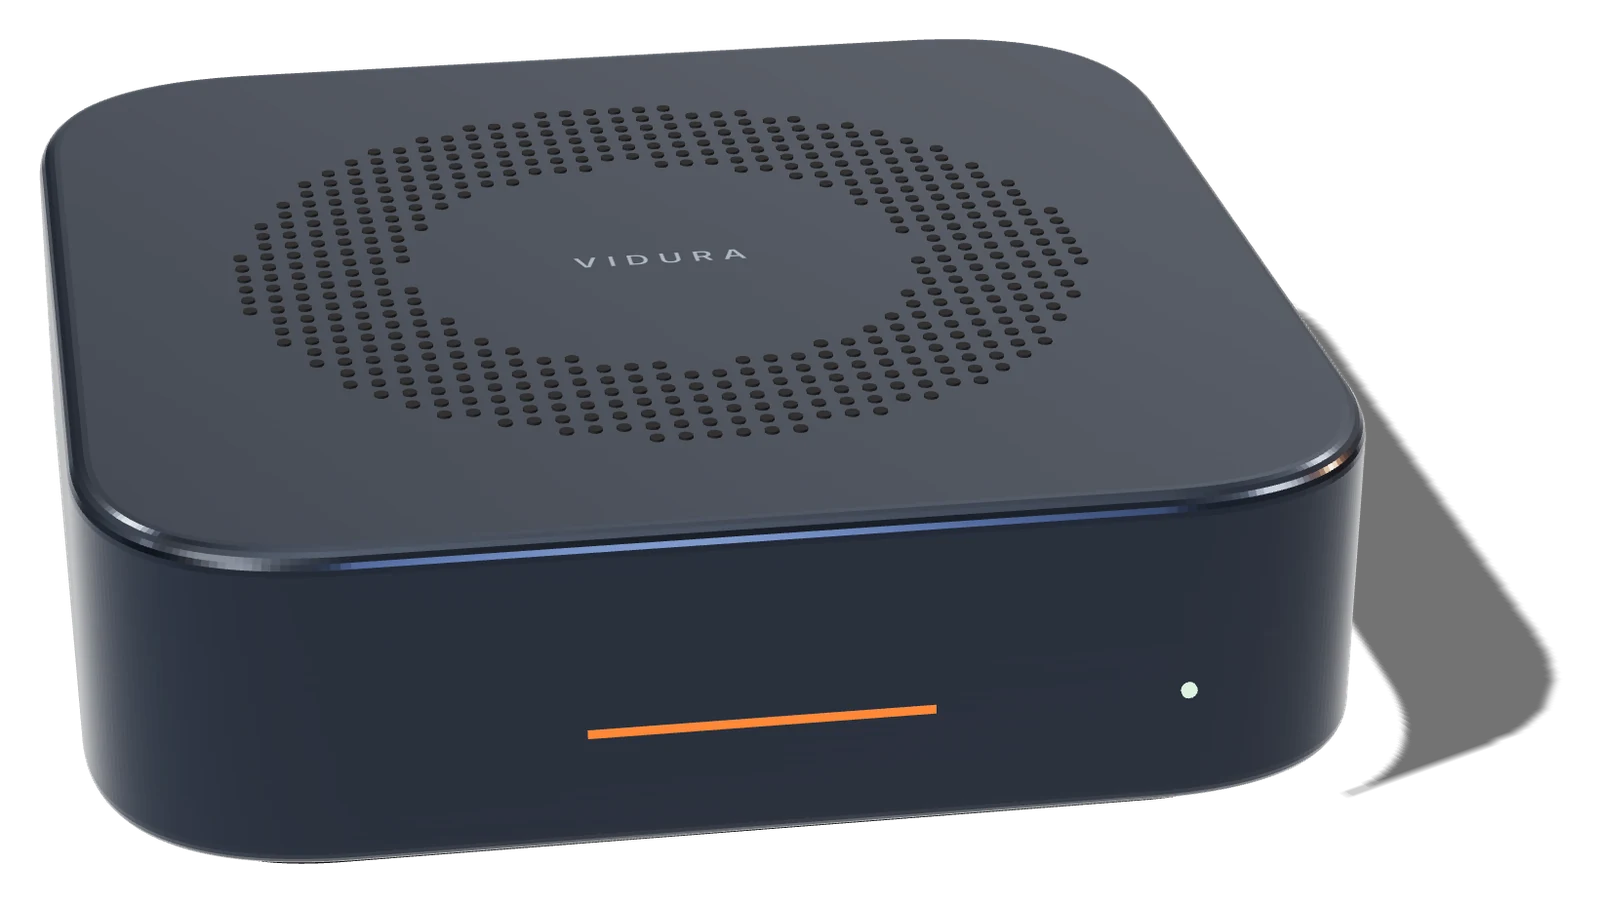
Vidura Edge, design renderDESIGN RENDER
Compact · protects your complete network

Vidura Edge

A small sealed box that connects to your network and protects all of it: servers, laptops, cloud, Wi-Fi, cameras and every connected device. Connect power and one network cable, and it starts watching.

—Designed to do the work of 1–2 expert cybersecurity analysts
—Plug in and protect in minutes
—Gunmetal machined metal chassis
—Works fully offline when required
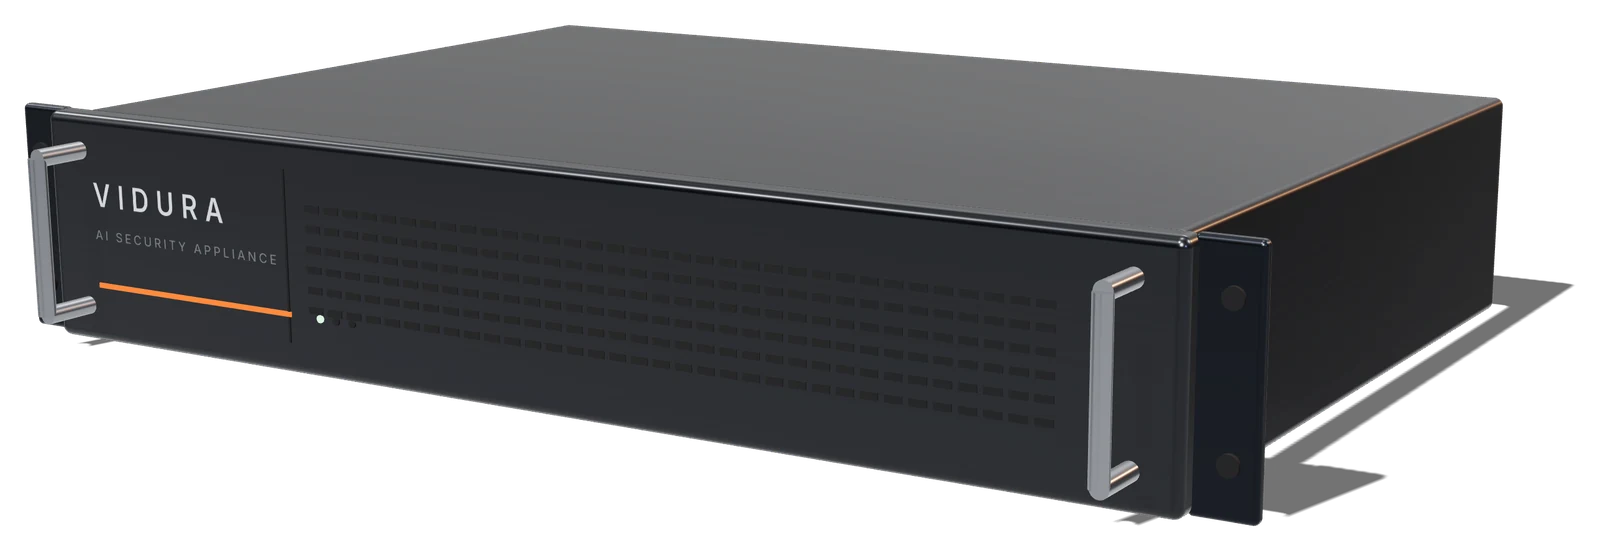
Vidura R, rack-mounted, design renderDESIGN RENDER
Larger · rack-mounted for big networks

Vidura R Coming soon

The larger Vidura, mounted in your server rack beside the firewall. Built for large organisations with many sites, it watches the whole estate, including every branch that runs a Vidura Edge.

—Designed to do the work of 5–7 expert SOC analysts
—Standard rack mount, front handles
—Runs the AI, data store and console on site
—One console across Vidura Edge and Vidura R
▶ Watch it work

Three common attacks, played out on a typical network.

Animated scenario · sample network
{{ nd.code }} {{ nd.label }}{{ nd.sub }} {{ nd.tag }}
Step {{ scnNum }} of {{ scnTotal }}
{{ scnCap }}
{{ scnSub }}
VIDURAnow
{{ phone.title }}
{{ phone.body }}
› {{ phone.a1 }}› {{ phone.a2 }}› Undo available
✓ Approved · applied
How to read the map
{{ lg.label }}
One console · five views · choose your role

The screen your team would use.

Illustrative console · sample organisation · not live data
Vidura / Sample Co-operative Bank
Monitoring · 9 of 10 sources healthy On-prem · Mumbai DC
{{ mapTitle }}
{{ lg.label }}
{{ ni.label }}{{ ni.type }} · {{ ni.zone }}
{{ ni.status }}
In plain words
{{ ni.note }}
Where Vidura gets this
{{ ni.sees }}
Click any box to see what Vidura knows about it, or ask a question on the right and watch the map light up.
Security score
72/ 100
▲ 11 points in 12 weeks · Fair
This week, from noise to decisions
{{ f.label }}{{ f.n }}
Score by area
{{ a.label }} {{ a.v }}
Three things that need attention today
Daily brief · sent 07:00
{{ x.title }} {{ x.sev }} priority
What happened
{{ x.what }}
Why it matters
{{ x.why }}
What to do
{{ x.todo }}
Confidence
{{ x.sure }}
Waiting for your approval
{{ pendingCount }} pending · approve from desktop or phone
{{ ac.title }} via {{ ac.via }} · {{ ac.caseRef }}
{{ ac.risk }} impact
Why
{{ ac.why }}
Effect
{{ ac.effect }}
How to undo
{{ ac.undo }}
{{ ac.statusText }}
Alerts, triaged by AI
Last 3 hours · 6 of 612 shown
Time Source What the AI saw Verdict Confidence
{{ r.t }} {{ r.src }} {{ r.title }} {{ r.verdict }} {{ r.conf }}
1,284
Assets in inventory
14
Open fixes from scans
Sat 02:00
Next approved scan window
3
Access grants expiring this week
Case #2417 · opened 01:47 · 6 alerts grouped Stolen password used to copy loan files
Likely malicious Confidence 92%
Attack path
{{ p.kind }} {{ p.label }}
Timeline · select a step
Evidence · {{ cur.t }} · {{ cur.src }}
{{ cur.title }}

{{ cur.finding }}

Query the AI ran
{{ cur.query }}
{{ cur.tech }}
Why this verdict
Three independent sources (email, sign-in and file-share logs) point to one user and one laptop within 25 minutes.
What would change it
If the employee confirms the weekend download and the new device, confidence falls and the case is closed.
7
AI apps & agents found
2
Not approved
1
Agent with more access than it needs
{{ stoppedCount }}
Stopped by kill switch
AI app or agent Used by What it can reach Status Kill switch
{{ ag.name }}
{{ ag.kind }}
{{ ag.users }} {{ ag.reach }} {{ ag.status }}
Agent ledger · every action, logged
{{ l.t }} {{ l.text }} {{ l.res }}
Ask anything
Ask in plain language. Answers come from your own data, with links to the evidence.
{{ askQ }}
{{ askWorking }}
{{ askHead }}
›{{ al.text }}
📎 {{ ev.label }}
Try asking

Try it: approve the actions in Operations, or stop the AI add-on in AI & agents, then return to the map.

How it works

AI proposes. Policy enforces. People decide.

1Connect
Read-only access to the security tools you already own.
2Watch
AI reviews every alert, 24×7, on your own hardware.
3Explain
A network map, a security score and plain answers.
4Act, with approval
Every change is logged and can be undone.
Console Status · Operations · Investigation · Ask
AI agents on your hardware
Triage Scanning Response AI governance
Data store
Logs and alerts from every tool, a list of every device, full history
Policy engine
The only part that can make changes: checks approval, keeps a rollback, logs every action
Connectors to tools you already own
SIEMEDRFirewallIdentityScannersCloudAI apps
Capabilities

Read-only first. A clear path to full response.

Each stage starts only when the one before has proved itself with design partners. The console above shows the full design.

{{ cp.n }} {{ cp.status }}

{{ cp.title }}

{{ cp.text }}

You set the limits

Choose how much the AI may do on its own.

Start read-only and allow more as trust grows. High-impact changes always need a person.

{{ ar.label }} {{ ar.mode }}

Every change is designed to be saved before it is applied and reversed in one click. Scans run only on approved systems, at approved times, with safe settings by default.

Built for AI-era threats

Familiar attacks, now faster. New risks created by AI.

{{ th.tag }}

{{ th.title }}

{{ th.how }}

Works with what you own

Official vendor connections. Nothing to install on your computers.

Each tool gets its own limited-access account, never a shared administrator sign-in.

Reading data is automatic. Any change goes through the policy engine and, above the risk level you set, needs a person to approve it.

Support for your exact products and licences is confirmed before contract.

{{ ig.cat }}{{ ig.can }}
{{ it.n }}
Sovereign by design

Your data and models stay in India.

The same console and AI, deployed where your rules require. Your data is used to improve the models only with your consent, and never leaves your premises.

On-premises

Vidura appliance

Vidura Edge (or Vidura R, coming soon), inside your own premises, runs the AI, the data store and the console. Designed so that nothing leaves your network.

Hosted

Indian cloud

A dedicated edition hosted in Indian data centres, for organisations without space for their own server.

Defence & strategic sites

Fully air-gapped

Designed to run with no internet connection. AI and threat updates arrive as signed packages through an Indian-owned channel.

CERT-In ready

Audit evidence gathered all year. Draft incident reports within hours.

DPDP Act

A record of who accessed personal data, kept as it happens.

RBI, SEBI & IRDAI

Scanning between periodic audits, in support of your CERT-In-empanelled auditor.

Board report

Two pages each month, written for directors.

Before you buy any AI SOC

Seven questions to ask. Our answers.

Industry analysts recommend judging AI SOC products on results, transparency and limits on automation, not on demonstrations. Ask every supplier these questions, including us.

What we are not
Not another firewall or antivirus. We make the ones you have work together.
Not a black box that acts alone. Every action is explained and approved.
Not a foreign cloud service. Your data and models stay in India.

{{ fq.a }}

AI SOC editions

Start with visibility. Add more when you are ready.

Annual subscription, priced by the number of monitored devices or users. The server is sold or leased separately.

Edition 01

Visibility

Read-only connections, the network map and status views, scheduled scanning and compliance reports.

Edition 02

AI SOC

Everything in Visibility, plus AI review of every alert, approved response actions, and automated firewall-change and access requests.

Edition 03

Sovereign

Everything in AI SOC, on your premises or fully offline, plus control of AI tools and agents and a sensor for critical computers.

Add-on

Managed 24×7

Mudra analysts working alongside the AI, 24×7, for organisations without their own security staff.

Design-partner programme

Judge it on your own alerts.

We are working with a small group of organisations to shape Vidura. Connect it read-only, run it alongside your team and compare its verdicts with your own. Nothing in your network is changed.

WEEK 0Connect read-only to your log platform, firewall, endpoint protection and scanner, using limited-access accounts that you control.
WEEKS 1–3Daily brief and live triage on current and past alerts. Your team marks each verdict right or wrong.
AT THE ENDAn accuracy report you keep: verdicts compared with your team’s, threats missed, time saved, and a summary of what is exposed.
Vidura earns access step by step: read-only first, changes last.
03 — What we do

Nine services. One accountable partner.

All solutions →
01

Managed detection & response

Continuous monitoring of network, endpoint and cloud activity. Vidura, our AI SOC, reviews every alert. Named analysts handle escalations and help contain threats.

02

Zero-trust network access

Replace broad VPN access with per-application access based on verified identity. Contractors and remote staff reach only the systems they need.

03

Data loss prevention

Classify sensitive data and monitor how it moves: USB, webmail, cloud storage and archives. Helps detect accidental and deliberate data leaks.

04

Cloud security (CASB & SASE)

Cloud access security broker (CASB) and secure access service edge (SASE): one security policy for cloud applications, private applications and internet access, applied close to the user.

05

OT & IoT security

Protection for operational technology (OT) and connected devices (IoT) in plants, substations and buildings. We start with passive discovery, then segment networks, then plan patching.

06

Ransomware readiness

Immutable backup, tested restore, segmented recovery and a rehearsed response plan. Recovery time is a key measure of ransomware readiness.

07

Network & perimeter engineering

LAN, WAN, wireless and private 5G networks, designed and installed by a team delivering large-scale network projects since 1997.

08

Data centre, DR & storage

Compute, storage and disaster recovery, designed and regularly tested so failover works when it is needed.

09

Command & control (C2, C4I)

Command-and-control (C2) and C4I control rooms for defence and government programmes, designed to stay operational if a single link fails.

Not sure which of these you need? Start with a two-week security assessment and we will give you a clear recommendation.

Book it →
04 — How we engage

We integrate before we replace.

STEP 01

Assess

A two-week review of your systems: asset discovery, exposure mapping, control gaps and compliance status. You receive a findings report suitable for senior management or auditors.

STEP 02

Design & deploy

A roadmap prioritised by risk and budget. We integrate what you already own before we recommend anything new.

STEP 03

Run

Managed monitoring, patching and response under agreed service levels, with engineers working alongside your team for an agreed period.

Where we work

Sectors where downtime has serious consequences

Defence
Public sector & PSU
State & smart-city programmes
Banking & financial services
Healthcare
Higher education
Industrial manufacturing
Energy & utilities

Two weeks. Fixed scope. Findings you keep.

A two-week assessment with a fixed scope and no obligation. You keep the findings whether or not you continue with us.

Start the conversation→
Solutions

Services built around your risks.

Nine services, mapped to the five stages of managing cyber risk, so you can see where each one fits. Every engagement starts with your existing systems: we integrate before we replace.

How to read this page

Each service supports one of five stages.

01 Identify

Understand what you own and what is exposed before investing. The Assess package starts here.

05 — OT, ICS & IoT protection
02 Protect

Reduce the ways in, and prevent sensitive data from leaving.

02 — Zero-trust network access
03 — Data loss prevention
04 — Cloud security, CASB & SASE
07 — Network, wireless & 5G
03 Detect

Continuous monitoring by analysts who know your environment.

01 — Managed detection & response
04 Respond

A tested response plan and experienced responders.

09 — Command & control (C2, C4I)
05 Recover

Recovery times that have been tested, not assumed.

06 — Ransomware readiness & recovery
08 — Data centre, DR & storage
How it is packaged

Three ways to engage. Each scoped before contract.

Tier 01

Assess

A fixed two-week engagement. You receive a findings report, a prioritised risk register and a costed roadmap.

Asset & exposure discovery
Control-gap analysis
Compliance posture review
Management summary
Tier 02

Managed

Ongoing monitoring and response under agreed service levels, with a named analyst team and monthly reporting.

24×7 detection & AI triage
Vidura AI SOC console included
Agreed response times
Patch & vulnerability cycle
Quarterly posture review
Tier 03

Build

Project-based integration of networks, data centres, disaster recovery and C4I systems, delivered against milestones with a senior project manager accountable.

Design & bill of materials
Supply & installation
Commissioning & handover
Annual maintenance & support options
01

Managed detection & response

Our managed detection and response service monitors activity across your network, endpoints, identities and cloud environments. Security analysts investigate alerts, prioritise genuine threats and recommend response actions. Monitoring coverage, escalation procedures and response commitments are defined in the agreed service levels.

What is included
24×7 monitoring Threat intelligence Agreed response times Forensic reporting
02

Zero-trust network access

A broad VPN can give a compromised laptop access to much of your network. We replace it with per-application access based on verified identity and device health, so a contractor reaches only the system they need and an attacker’s ability to move across the network is greatly reduced.

What is included
Identity-aware proxy Device posture Micro-segmentation Privileged access
03

Data loss prevention & insider risk

We start by classifying sensitive data, then monitor how files move across your network and out to cloud storage, webmail, USB and messaging. Renamed, modified or archived files can be tracked, and optional behaviour analytics highlight patterns that often come before deliberate data theft.

What is included
Data classification Egress control User behaviour analytics DPDP Act readiness
04

Cloud security, CASB & SASE

Many organisations use several cloud services without a clear view of what is exposed. We identify the software-as-a-service (SaaS) and infrastructure (IaaS) services in use, apply one consistent security policy, and give you a single view of cloud threats, without routing all traffic through a central data centre.

What is included
Shadow-IT discovery Posture management Secure web gateway SD-WAN
05

OT, ICS & IoT protection

Operational technology (OT) and industrial control systems (ICS) often cannot be restarted for patching. We start by passively identifying controllers, sensors and building systems on the network, map the boundary between IT and OT, and segment it, so a compromised office account cannot easily reach a plant floor. Designed for environments where availability comes first.

What is included
Passive asset discovery IT/OT segmentation Protocol inspection Industrial-grade networks
06

Ransomware readiness & recovery

Prevention reduces risk; recovery capability limits the damage. We build immutable, isolated backups, protect the recovery path from the rest of the network, and rehearse restoration until the recovery time is known. Early detection can save hours; a tested response plan can save days.

What is included
Immutable backup Tested restore Tabletop exercises Incident retainer
07

Network, wireless & private 5G

Network engineering has been part of Mudra since 1997. We design, install and support LAN, WAN, campus and warehouse wireless, and private 5G networks, with security built into the design from the start.

What is included
LAN / WAN design Enterprise wireless Private 5G Structured cabling
08

Data centre, DR & storage

Business-continuity infrastructure across separate physical and cloud sites, sized to your recovery point and recovery time objectives (RPO and RTO). Includes tamper-evident archival storage for organisations with legal record-keeping requirements.

What is included
DR design RPO / RTO modelling Archival storage High-performance compute
09

Command & control (C2, C4I)

Command-and-control (C2) and command, control, communications, computers and intelligence (C4I) systems for defence and government. Decades of work with the Armed Forces have given us specialists who understand how these systems are used. Requirements are defined with end users, built by in-house engineers and validated feature by feature before delivery.

What is included
C2 / C4I systems Secure voice & video Tactical comms Field validation
Start where you are

Where would you like to start?

“We don’t know how exposed we are.”

Start with a two-week security assessment. Fixed price, no commitment, and you keep the findings.
Book an assessment →

“We have the tools, but not the people to monitor them.”

Vidura AI SOC, using the tools you already own, with our analysts available 24×7. Start read-only as a design partner.
Talk about Vidura →

“We have a project and a deadline.”

Network, data centre, disaster recovery or C4I projects, delivered against milestones with one senior project manager accountable throughout.
Scope a project →

The capability behind the service

Delivery and support are handled by our own teams.

24×7
Monitoring coverage
80+
Qualified engineers & analysts
500+
Deployments delivered
1
Named delivery manager for every engagement

Tendering? We respond to RFPs and EOIs across public and private procurement worldwide.

Send us the tender reference and we will confirm eligibility, relevant past performance and OEM authorisations, usually within two working days.

Submit a tender enquiry→
Company

From computers in 1987 to Argus today at the border.

Mudra Electronics was founded in 1987 to supply computer peripherals and began manufacturing its own machines in 1989. Network integration followed in 1997, and later cybersecurity services. Today we apply that engineering experience to rugged AI hardware, starting with Argus.

1987
Founded — computer peripherals
1989
Manufacturing our own machines
1997
Large-scale network integration
Now
AI cameras — Argus
“We build for places where a missed alert costs more than a missed deadline.”
Abhinav Bharat Shetty
Chief Executive Officer
500+
Deployments delivered
30+
Defence & government entities
80+
Engineers & analysts
ISO 9001 · 27001
OSCP · CISSP · CEH engineers
Careers

Help us build Argus.

New Delhi, Dehradun and Bengaluru. Select a role to apply by email.

{{ r.title }}
{{ r.team }}
{{ r.city }}
→
Contact

Tell us what you need to protect.

Or write directly to mel@mudraindia.com.

Your mail app should have opened.

Press send there and we’ll reply within one working day. If nothing opened, write to mel@mudraindia.com.

Head office

Mudra Electronics Ltd.
LG-4, 5 & 6, Somdutt Chambers-II
9 Bhikaji Cama Place
New Delhi 110066

Offices

New Delhi · Dehradun · Bengaluru